Why Third-Party Analytics Become a Weak Link
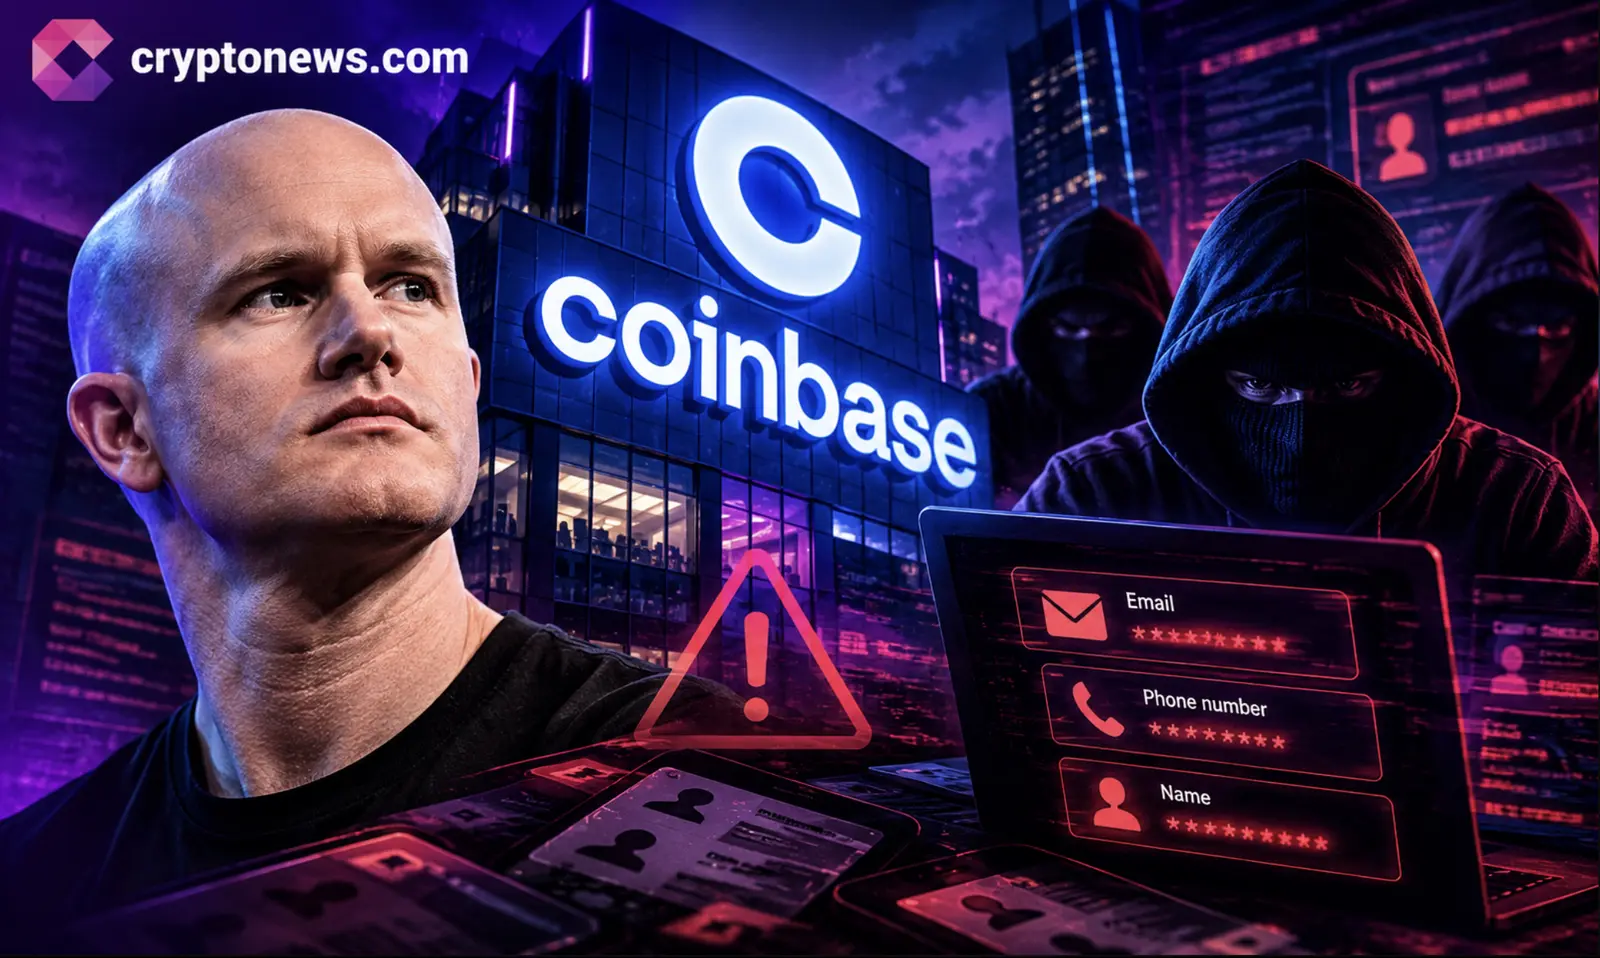
A data breach at analytics provider Amplitude exposed contact information for a small subset of Coinbase customers. The incident occurred after Coinbase integrated Amplitude for product analytics. Affected users received notification emails detailing the scope of the exposure.
Breaking news
 SAT Japan Enables Stablecoin Payments for Overseas Car Buyers
 Ethereum Powers Digital Public Infrastructure for Sovereign Services
 Crypto.com Exits Hong Kong Retail Market
 South Korea Pushes Exchanges Toward Greater Cold Storage After Binance Breach
The breach highlights a critical gap in crypto security thinking. Many users assume that holding keys in a hardware wallet guarantees safety. However, if the exchange or third-party service holding your email and phone number is compromised, attackers can target you with phishing or social engineering. Self-custody protects the funds, but not your identity data.
Coinbase partnered with Amplitude to track user behavior on its platform. This integration meant customer contact details were stored outside Coinbase's core infrastructure. When Amplitude suffered a breach, that data was exposed. The incident mirrors a similar event involving Ledger, where customer information was leaked through a third-party provider.
What Should Crypto Users Do Now?
Security experts note that crypto assets are only as safe as the weakest link in the chain. A hardware wallet secures the private key, but a compromised email address allows attackers to reset passwords or intercept 2FA codes. The Coinbase case shows that self-custody must be paired with strong email security and awareness of third-party data flows.
Users should audit their email accounts for phishing attempts referencing the breach. Enable two-factor authentication on email and exchange accounts. Rotate passwords for any service that shared data with the compromised provider. Monitor bank and crypto accounts for unauthorized transactions.
Frequently Asked Questions
The broader lesson is clear: crypto security is not just about holding your own keys. It also requires protecting the digital identity tied to those keys. As more exchanges and wallets integrate analytics tools, the attack surface grows. Users must treat their email as a critical security asset, not just a login credential.
Did the Coinbase breach expose private keys or transaction history? No. The Amplitude incident exposed contact information such as email addresses and phone numbers. It did not reveal private keys, seed phrases, or detailed transaction histories.
How is this different from a typical exchange hack? Unlike a direct exchange hack, this breach came from a third-party analytics provider. The funds themselves were not at risk, but the exposed contact data increases phishing and social engineering risks for affected users.